Safer internet access: Web content filtering and TLS inspection
A large part of daily work takes place in the browser: cloud applications, research, supplier portals, online banking. At the same time, the browser is the most common route through which malware and fraud attempts enter the company.
The classic example is the deceptively real sign-in page where someone enters their access data. There are also manipulated downloads, hijacked websites and services that employees use with the best of intentions without IT even knowing about it.
Protection on the device alone is too limited here. A stolen login on a spoofed page is not technically malware that a virus scanner could detect, and an unauthorized cloud service does not affect the end device at all. Effective protection only becomes effective when it is evaluated where a connection actually goes.
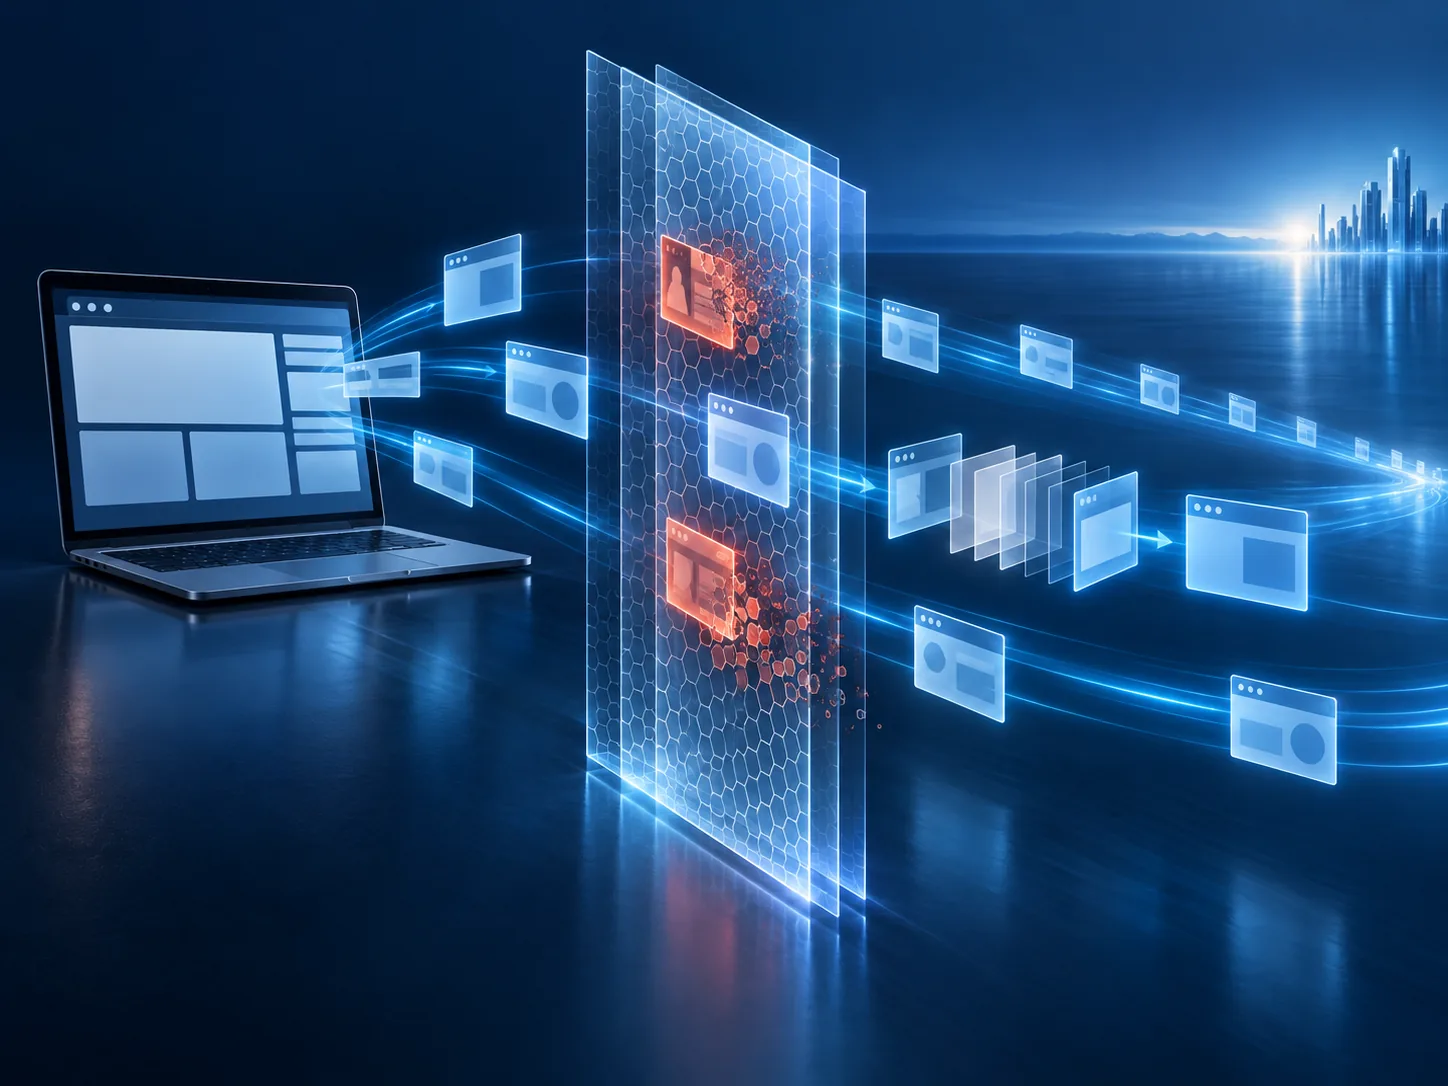
Effective protection when surfing is not achieved by a single product. The individual layers do not stand independently side by side either; they build upon one another: the more precisely something is to be tested, the more visible the data traffic must be.
Web category filters work by categorizing websites and domains into defined categories such as social media, gambling, malware, or file sharing. When a website is accessed, it is checked which category it is assigned to, and access is allowed or blocked according to the company's policies.
The strength of this approach lies in its simplicity and centralized control. Companies can selectively restrict access to specific web categories without having to manually maintain individual websites. However, the limitations lie in the accuracy of categorization: the evaluation usually takes place at the level of the website or domain, not based on the specific content of a single page. However, for most of the unwanted or risky targets, this is already sufficient.
If there is to be differentiation within a website, for example, one section is allowed and another is blocked, the domain name is no longer sufficient. With HTTPS, the rest of the address is encrypted, and without additional measures, a security system on the network only sees which server is being spoken to.
That is exactly what TLS Inspection is for: The connection is controlled to be broken, the content for the inspection is made visible, and it is then re-encrypted and forwarded on. The important thing is the right expectation: Decryption itself does not detect anything. It merely makes the traffic accessible for the subsequent checks. What is ultimately detected and blocked is determined by the inspection mechanisms used, and the protection on the device remains necessary in the meantime.
TLS Inspection therefore deserves a deliberate decision, also due to its side effects. A corresponding certificate must be distributed on the devices, and applications that expect an unchanged connection may refuse the service in this case. A test with the business-critical applications is therefore part of the introduction. For reasons of data protection, categories such as health, finance, and government are usually exempt from the inspection. These exceptions are documented, and the workforce should know that it is being examined and to what extent.
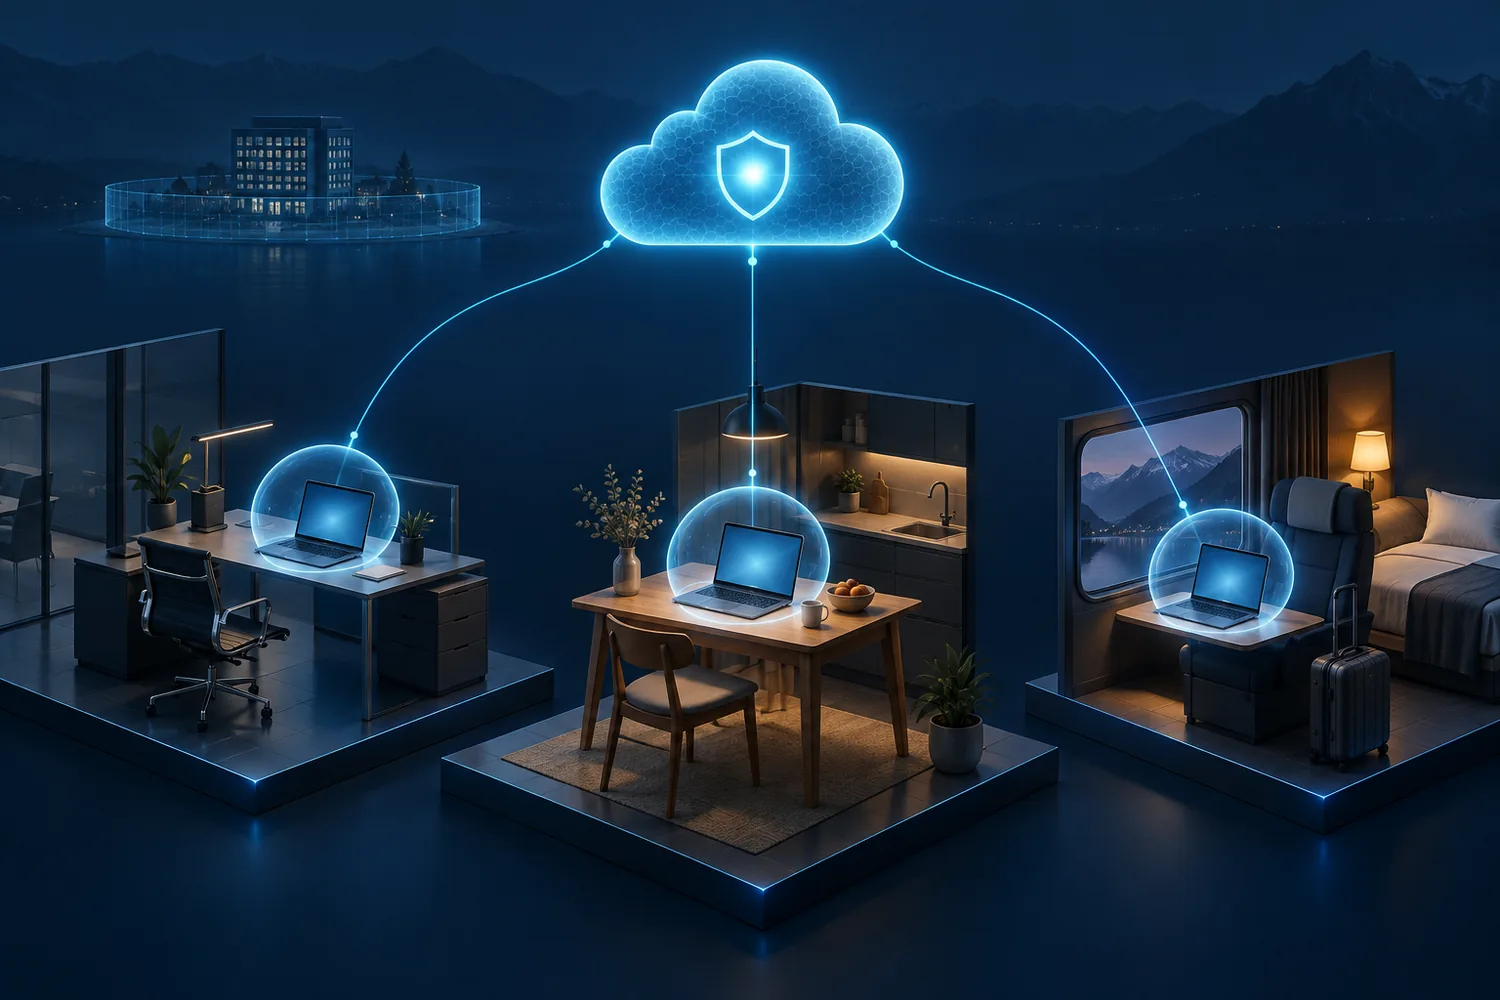
In the past, access to the Internet could be secured at one point, namely where the company network ended. This network connection still exists, but it only covers a part of the work. Work is done in the office, at home, in hotels, and on the go, and the applications used are anyway in the cloud.
Therefore, protection must be tied to the device and the identity, not to the location. Today, the web filter from Microsoft Defender for Endpoint is widely used: it blocks websites by category directly on the managed device, in the office or on the go. Microsoft Entra Internet Access, part of Microsoft Global Secure Access, extends this approach: a client on the device routes web traffic through the security service, regardless of the network the device is currently located in. The rules remain the same whether someone is at the workplace or working on the go.
A practical side effect: Because the policies are tied to identity, different rules can be applied to different roles without having to build separate network segments for that purpose.
In discussions, the individual protection mechanisms are often mixed together. This overview organizes them. The tasks are deliberately overlapping.
| Protection mechanism | Where does it work? | Typical task |
|---|---|---|
| Firewall | on devices, across network boundaries, or in the cloud | Controls connections according to rules |
| Web filtering | on the web gateway, on the device, or in the browser | evaluates goals and categories, depending on the equipment, also content |
| Endpoint protection | on the device | checks files, processes, and, depending on the product, web requests |
| Email protection | in the email flow and depending on the product when the link is called up | reviews news, attachments and links |
The four levels do not replace each other. A link from an email that is harmless at the time of delivery and only shows a fraud page hours later will not be blocked upon receipt. It can be re-checked upon clicking, either through the link protection of the email security solution or through web filtering.
Technical measures only work if it is clear what applies within the company. A clear regulation regarding internet use answers the questions that actually arise in everyday life:
In many companies, the handling of AI services is particularly unregulated, even though it is already taking place. The regulation should specify which services are allowed, what data should not be collected there, and how to request an exception. Technical restrictions support this where the risk warrants it.
The second part concerns logging, and here carefulness is warranted. Logs from a web protection service can connect users and the targets they target. Therefore, for ongoing analysis, summarized or anonymized data should be used wherever possible. Personal analysis needs a defined purpose, strictly limited access rights, and an appropriate retention period.
Employees must be informed in advance about what and to what extent the investigation is being conducted. Monitoring that serves only to observe behavior is inadmissible in Switzerland.
Web filtering is not a measure that you set up once and then forget about. Regular charges occur during operation:
As experience shows, the quality of this ongoing maintenance determines whether web filtering is accepted or perceived as a hindrance and circumvented.
A well-connected solution causes only minor additional delays. Whether these are noticeable in everyday life depends on the location, connection, and the applications used, and is tested with the typical applications in the pilot.
Certain services and categories can be blocked. However, a web filter cannot distinguish whether someone is accessing the same website privately or for business purposes. Therefore, a proportionate approach has proven effective: blocking clearly dangerous categories and conducting the rest through an understandable regulation.
Technically, the logs can connect users and targets. Whether and how this is evaluated is a conscious decision that must be determined and documented. For ongoing monitoring of the security situation, summarized evaluations without personal reference are usually sufficient.
Entra Internet Access also protects outside of the office, as long as the client is active on the device and the relevant traffic is routed through the service. The protection thus depends on the device and the identity, not the location.
No client can be assumed to be installed on unmanaged devices. The way around this is through access policies that restrict access to company data on such devices.
Secure internet access arises from the interplay of domain and category filters, the more rigorous examination of encrypted traffic where necessary, device protection, and clear usage regulations. No single component is sufficient.
An inventory shows which accesses are protected today, where there are deliberate exceptions, and who regularly checks them. It was completed in a few days and provides a reliable basis for the next steps.
In any case, there remains a residual risk. New malicious targets are not yet assigned to any category shortly after their creation; traffic deliberately excluded from the examination is not subject to substantive control; and a user account that has been taken over is within the permitted limits. Therefore, attentive employees and a functioning reporting mechanism are just as important as the technology.
You want to know how well your employees are protected when surfing today? Intecso AG will review the existing web protection with you and configure the appropriate filters as part of Managed Security. Contact us for a non-binding conversation.