ZTNA instead of VPN: This is how modern remote access works
For many companies, VPN has been the standard way to access the corporate network for years. Anyone who works from home or on the go creates a connection and is thus online, as if they were in the office. That is exactly the problem.
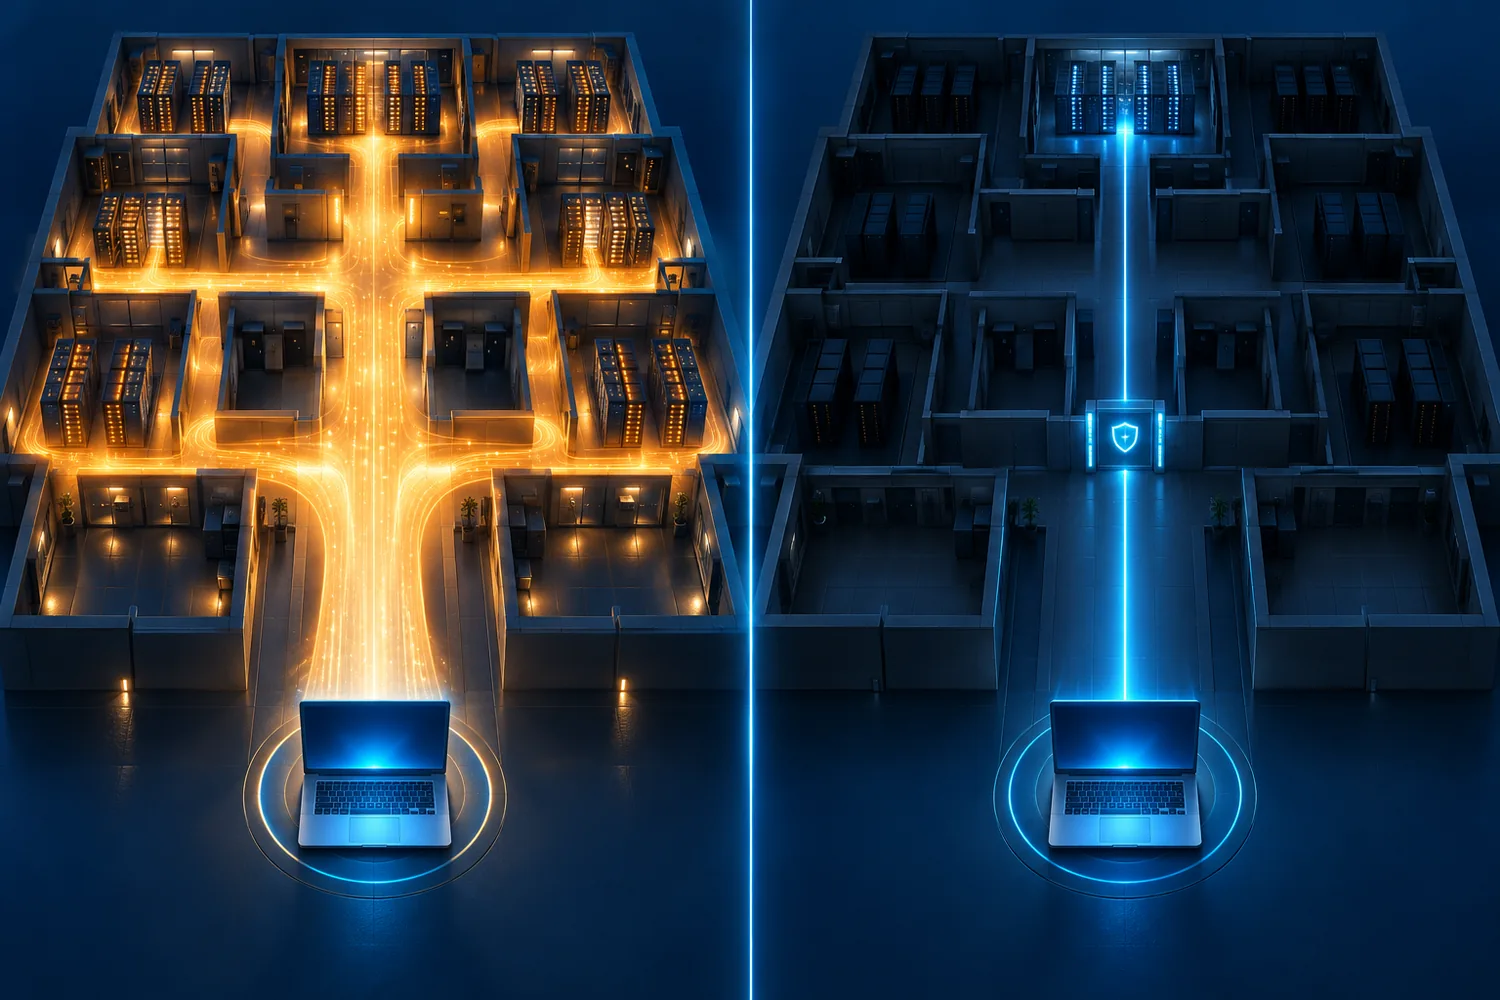
A widely deployed VPN makes more internal systems accessible than a single person needs for their work. If access falls into the wrong hands, such as through stolen login credentials or a compromised laptop, the attacker has the same access as an employee. They can then move around the network and search for lucrative targets.
To be fair: this is not a mandatory feature of the technology. A VPN can also be segmented, linked to device testing, and configured so that only the necessary traffic passes through the tunnel. In practice, however, many connections that have grown over the years are left open wider than they should be, and no one has the mandate to regularly verify this.
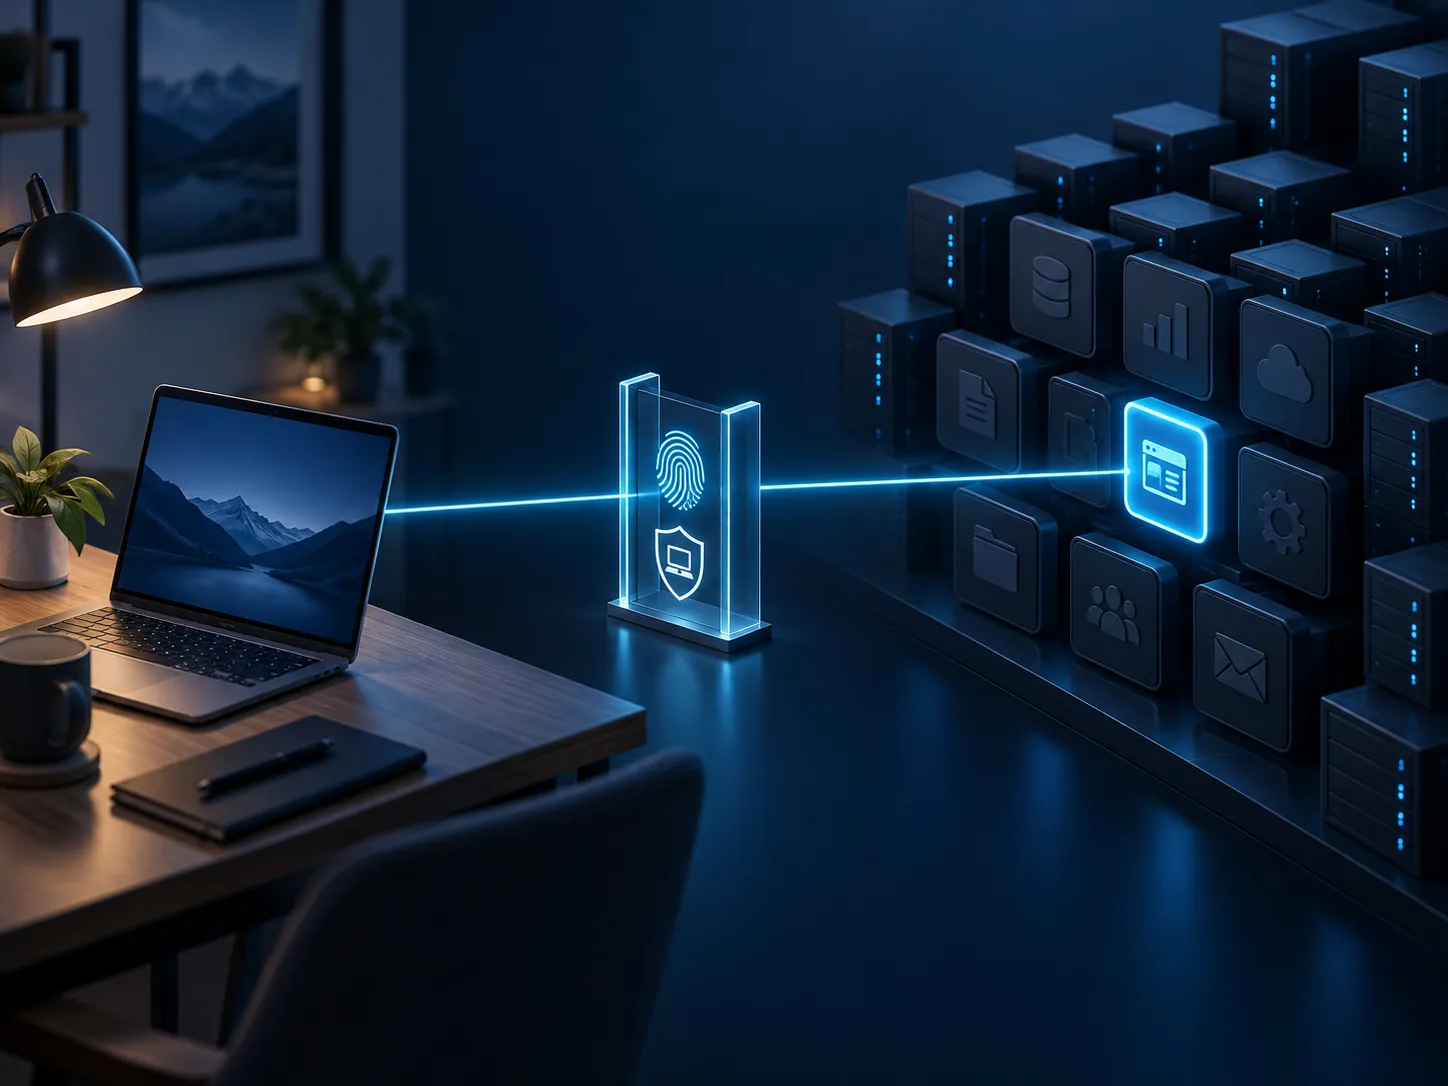
Zero Trust Network Access, or ZTNA, turns this principle on its head. Instead of allowing anyone to access the network, access is granted only to the one application that is needed. Everything else remains invisible.
Before any access is granted, the system evaluates the configured signals: Who is accessing, from which device, and does this device meet the stored requirements? Only when identity, device status, and authorization match, will the connection be established, and only for this one application.
The testing does not end with the registration. In supported applications, events such as a locked account or a changed device state can trigger a re-evaluation and terminate access. Which events are recorded and how quickly this happens depends on the client, the policies, and the scope of functionality and are among the points that are deliberately set at the time of implementation.
The most important difference in everyday life: Only the explicitly authorized resources are accessible through this access point. A bookkeeping group only gets access to the application it needs, not to all the servers in the same network. The more narrowly the permissions are tailored, the fewer entry points remain for an attacker who has taken over an account.
The following comparison compares a widely deployed classic remote access VPN with an application-specific ZTNA access. Several points on the VPN side are configuration issues, not technical limitations.
| Characteristic | Classic VPN | Zero Trust Network Access |
|---|---|---|
| Access to | Network areas, depending on the segmentation | Selectively released resources with restrictions on e.g. FQDN, IP address and ports |
| Examination | mostly when establishing connections | with each access, review depending on function |
| Equipment status | depending on the solution and configuration | a permanent part of the directive |
| Accessibility | as far as the network is open to the public | only what is explicitly disclosed |
| Lateral movement | dependent on the segmentation | severely restricted due to tight restrictions |
| Cloud applications | Alternative route in case of complete blockage | Traffic control can be controlled specifically |
| Access by partners | usually own network access | Targeted release per application |
| For employees | connect manually or automatically | runs in the background as a client app |
For companies that already work with Microsoft 365, Microsoft Entra Private Access is the obvious choice. The service is part of Microsoft Global Secure Access and uses the same identities and policies that already apply within the company.
The path of a connection can be described in four steps. On the employee’s device, a client forwards the intended traffic to the Microsoft cloud service. There, Entra ID and conditional access check, based on user, device, location, and risk assessment, whether access is allowed. If it is, the cloud service routes the connection to a connector, a small connection service within the corporate network. This performs the final step as an internal resource.
The connector builds its connection to the cloud service from there. Therefore, no incoming connections from the Internet to the corporate network are necessary, which significantly reduces the attack surface compared to a publicly accessible VPN connection point. The outgoing connections required and the internal application ports must of course be allowed.
For employees, little has changed, and that is intentional: there is no longer any connection that needs to be established first. The application is simply there, in the office as well as in the home office.
A common concern is that ZTNA only works for modern web applications. This is not the case with Entra Private Access. The service operates at the network level and can therefore also capture access that was tied to the VPN for years: file sharing via SMB, remote desktop, and SSH. Domain controllers can also be connected, allowing the login to internal applications to work via Kerberos without a VPN. The prerequisite is that name resolution and the required connections are set up correctly.
Separately, processes that require contact with the domain controller before the user logs on must also be considered: the Windows login itself, group policies, and password changes. Additional requirements apply for these, which must be verified for each environment. By clarifying these in advance, one avoids the unpleasant surprise that a device that is working outside the office cannot log on again. These restrictions primarily affect hybrid Entra ID Joined devices. With Cloud-only Entra ID Joined devices, the dependency on a local domain controller for user login is eliminated, which generally eliminates these challenges.
This eliminates further previous VPN use cases, provided the respective dependencies are examined.
The truth remains: Not every access can be switched immediately. In practice, there are cases where a VPN continues to operate in parallel for a period of time.
Parallel operation is not a failure, but rather the normal course during the transition. The important thing is to determine for each remaining VPN access whether and when it can be discontinued or continued as a documented exception. A forgotten VPN that no one monitors anymore is more dangerous than one that is deliberately operated.
A change does not begin with technology, but with an inventory of the current situation. In practice, this approach has proven effective:
The effort depends primarily on three things: the dependencies of the applications, the state of the device management, and the number of special cases. The most important factor is careful inventory taking, because what is overlooked at the beginning will be noticed later in operation.
In most cases, ZTNA completely replaces the VPN. Whether this also applies to you can be determined by testing the remaining applications.
Yes. Manual connection is eliminated, which increases user friendliness. Additionally, companies benefit from the direct integration with Microsoft Entra ID and Conditional Access.
In supported applications, such a change can trigger a re-check and terminate access. What events this involves and how quickly they take effect depend on policies and the client and are set at deployment.
Usually, yes. An existing Microsoft 365 environment already includes parts of the identity features; however, the access service itself must be licensed separately. What is present in your case and what will be added will be clarified in the inventory review.
External partners can also obtain application-specific access without access to the rest of the network. For this, identity, device, and client requirements must be met.
If a connector fails, other connectors from the same group take over. Therefore, they are designed multiple times from the beginning. If the internet connection of a location fails, external access is affected just as with a VPN.
The transition from VPN to Zero Trust Network Access is less of a technology project than a changed fundamental assumption: no longer does the situation in the network determine trust, but identity and device status at every single access point.
At the beginning, an inventory of the existing remote access services is presented. At the end, a list of the short-term accessible services, the remaining special cases, and the requirements that must be met are presented.
One final point that often gets overlooked: Even a properly configured ZTNA access does not protect against every risk. If someone assumes a legitimate account and device, the same permissions apply to them as to the legitimate person. Therefore, multi-factor authentication, endpoint protection, and the monitoring of suspicious access remain necessary.
You want to know which of your remote access services can already be converted today? Intecso AG supports Swiss SMEs from the initial assessment to the implementation of the new system. Zero Trust. Contact us for a non-binding conversation.